
GFF 2026 wrapped on September 11 at Jio World Centre with about a lakh of footfall, 1,200 speakers, and 100-plus regulators in the room. The official theme was agentic AI, tokenization, and quantum. The unofficial theme, if you sat in enough fraud and onboarding panels, was simpler: the attacker has automated, the regulator has noticed, and the defence has roughly six to nine months to catch up.
We attended around twenty sessions across the four days, from UIDAI’s product roadmap to the RBI Innovation Hub’s FinConnect pitches to the MAS keynote. This is what stuck, organised into the eight shifts we think a CRO, CCO, or head of onboarding should carry back to their strategy meeting.
1. Deepfakes have broken video KYC as a trust layer
The most repeated line across the fraud panels was some version of “human agents cannot tell anymore.” AI camera tools now replace the default camera feed in real time, so the person on your video KYC call may be a synthetic face stitched over a real name, and your agent has no reliable way to see it. Real-time deepfake video and voice now run on 4 to 5 billion parameter models that fit on a phone.
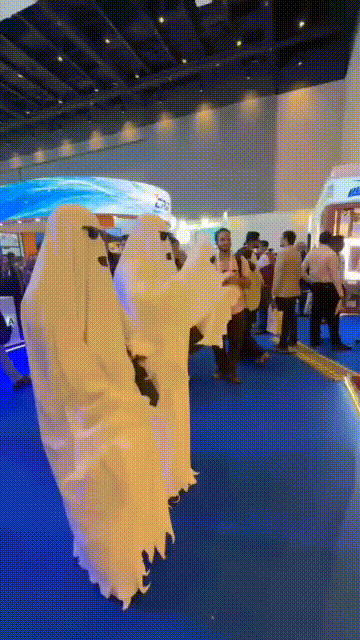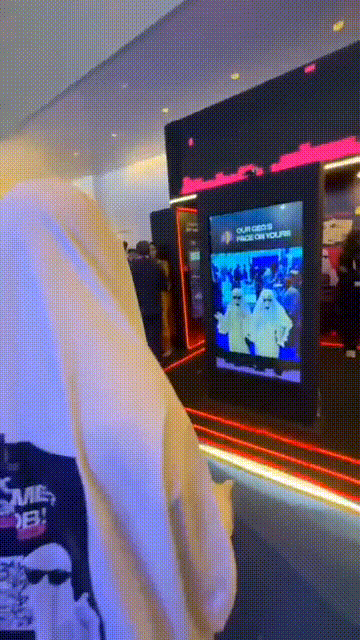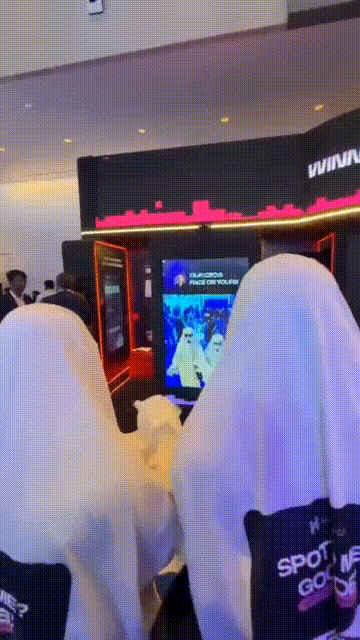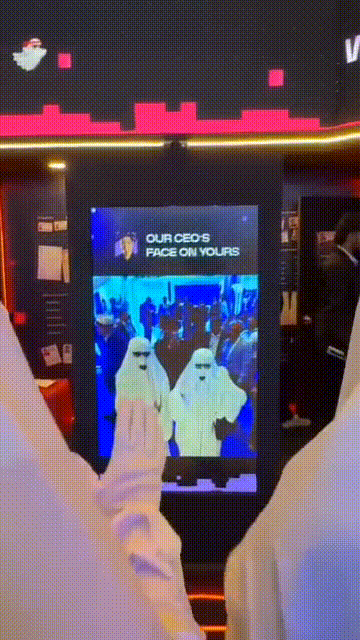
We ran a goofy yet impactful campaign at GFF this year called ‘Ghost In The System,’ calling out how ghosts (deepfakes and synthetic identities) may be slipping into your systems without notice!
The numbers cited in the ‘Deepfake and Synthetic Identity Fraud’ panel were blunt:
- deepfake fraud up 2,137% in a year,
- deepfake creation tools on the dark web up 356%,
- and AI components present in roughly half of all fraud cases in 2026.
Three viral deepfake videos alone, including fake investment pitches from Narayana Murthy and Elon Musk and a fake government scheme announcement from the Finance Minister, cost Indian citizens over ₹850 crore. Two companies paid $20 million or more each after fraudulent Zoom board calls. One Hong Kong firm lost $25 million on a single deepfake video call.
For anyone who checked the SEBI liveness box and moved on, standard liveness catches display attacks (a phone held up to a phone). It does not catch face swaps built with free consumer tools. Biometric data is also broadly compromised, with fingerprint, voice, and facial geometry data for crores of citizens reportedly circulating. Even iris is now flagged as a future risk via smart glasses.
The consensus answer was to stop chasing individual deepfake models and instead model the four or five fundamental generation techniques, so a new release from any lab is caught without retraining.
The moderator, Mr. Krishna Sastry Pendyala’s closing line was “use AI to kill AI-related problems,” something the RBI governor also stressed recently at FIBAC.
2. KYC is becoming “Know You Continuously”
Onboarding controls have improved enough that fraudsters have adapted around them. The pattern SBI and HSBC both described in the ‘Trust without Friction’ panel is “seasoning”: open a clean account, behave normally for three to six months, then activate it. Good accounts turn into mules post-KYC. A static risk category assigned at onboarding cannot see that.
Mule networks have grown from one hop in 2021 to 20-plus hops today, and the persona has diversified well beyond the assumed rural, low-income profile. Panelists described students in first jobs who are simply told to move small amounts in a specific pattern every day. India’s top banks reportedly sit on around five lakh uninvestigated fraud cases, and only 2 to 5% of victims are estimated to report at all.
The response is continuous monitoring across velocity, geography, transaction pattern, and behavioural drift.
Axis Bank’s CISO, Mr Vinay Tiwari, pointed out layering typing, speech, device driver, and session signals into a running risk score, with a branch visit triggered when the score is breached.
Mr. Indraneel Ajitkumar Pandit, CDO of Federal Bank, described behavioural biometrics (typing cadence, how the phone is held, thumb versus finger) as a continuous KYC layer, plus a knowledge graph built across partner traffic.
Mr Ravi Ranjan, MD, SBI, shared, “For the State Bank of India as a whole, last year my proactive risk management department saved 1.36 lakh accounts, and the total amount saved was 27,000 crores.”
Mr. Krishna Sastry Pendyala, Ex-Partner, EY, echoed other sessions quite aptly: “Know Your Customer is turning into Know You Continuously.” Onboarding is the first check, not the only one.
3. The golden window has shrunk from 15 minutes to 30 seconds
For years, the recovery benchmark after a fraudulent transfer was the “15-minute golden window.”
Mr Ranjan Bhattacharya, HSBC’s MD and Head of Group Strategy, called that obsolete and said, “15 minutes is probably too long. 30 seconds to one minute is the more realistic time frame because today APIs enable us to ping and take those decisions at lightning speed.”
The panel also agreed that UPI makes it harder than cards because money settles instantly with no temporary hold. Fraudsters move funds at exactly the speed the system allows.
That changes what detection has to look like. Rule engines respond instantly but cannot see behaviour. AI models can see behaviour but must do it at UPI scale, which Mr. Rahul Choube from VISA put at 30,000 transactions per second with millisecond latency in the ‘AI vs Fraud’ panel.
Mr Ajay Sharma, MD of HSBC, said they scan about a billion transactions a month for real-time anomalies. The recommended architecture was hybrid: AI reinforcing the rule engine rather than replacing decades of institutional logic, with a fallback if the model fails because banking cannot stop.
Two practical notes for anyone designing the customer-facing side.
- Over-blocking is a real cost: false positives on genuine customers erode trust as surely as fraud does.
- Framing matters. The panel agreed that a short hold presented as “your transaction is being reviewed for security” is well received, while the same hold presented as a “delay” is not.
4. Shared fraud intelligence is now live infrastructure
Find a vulnerability at one bank and the same attack hits the rest of the ecosystem the next day. Several speakers made that point, and it explains why fraud data-sharing stopped being a talking point this year and started shipping.
The pieces now in place: RBIH’s DPIP, a privacy-preserving registry of suspected fraudster accounts and mobile numbers that banks can query at onboarding or transaction time (PNB already uses it at account opening).
- I4C’s CFCFRMS links to every bank, so a 1930 or NCRP complaint can trigger a near-instant lien.
- MuleHunter for post-crime network detection.
- And IDPIC, in development, with credit fraud as the obvious next scope.
Lenders are also sharing fraud-attempt data through closed user groups, and more than one panelist asked for a financial crime bureau: block a bad actor once, and they stay blocked everywhere.
Regulation is forcing the pace. From January 2027, RBI shifts the burden of proof to banks: prove customer negligence, respond to unauthorised debit complaints within five days, and share compensation of up to ₹25,000.
Around seven countries already hold payment platforms liable for fraud losses, and speakers expect 17-plus. Telecoms and messaging apps, where most fraud starts, were told they should carry KYC obligations too.
The catch: most institutions still keep fraud, AML, cyber, and risk in separate silos. Connect those signals internally first. Sharing them externally comes after.
5. Agentic AI is in production, and the human still signs
ET’s post-event headline summed up the mood: AI was everywhere, full automation was not. Agents are running real work inside banks. What has settled is where they stop.
SBI’s deputy MD, Ms. Sukhvinder Kaur, shared the framework they use to decide: score each use case on impact, stakes, and reversibility.
- Low impact and fully reversible (account statements) gets fully automated.
- Medium impact, reversible at a cost (KYC documents up to a limit) gets a human in the loop.
- High impact, irreversible, or regulatory gets AI assistance with a human making the final call.
Their MSME lending system now underwrites up to ₹5 crore in under an hour and has processed ₹1 trillion on that basis, with the relationship manager freed from data collation rather than removed from the decision.
The engineering patterns for regulated agents were consistent across Federal Bank, IndusInd, and HSBC.
- Force structured, deterministic outputs (“verified / unverified”) rather than free text, because free text is where hallucination lives.
- Run checks in parallel (KYC, PEP, ownership, EPFO) instead of sequentially.
- Set confidence thresholds per decision type, since a single threshold for everything is an anti-pattern: a name match may need 98%+, a supporting field may not.
- Log observability at two levels: the intermediate tool calls and inferences (L1) and the final outcome and which system delivered it (L2).
- Keep accountability with the business unit that owns the customer, never with the AI team.
One US bank was cited running 260 agents and 140 “digital employees,” all reporting into business managers.
The Evals masterclass, by Mr Akshay Surve of Anthropic, added the discipline most teams skip.
- Roughly 80% of evals for agentic systems should be code-based checks (did it call the right tool, did the FOIR calculation include every EMI).
- LLM-as-judge belongs only to qualitative output, like catching an agent that promises approval “by end of day.”
- And for financial decisions, pass-all-at-K is the bar: every run must pass, not one in three.
Mr Rajiv Anand of IndusInd summarised in the ‘Co-Designing Responsible AI’ panel: “99% right is not good enough in banking.” A realistic near-term win, several agreed, is 70 to 85% productivity improvement, with P&L impact perhaps six to twelve months out.
For what it is worth, our own underwriting agents fit the same pattern. They pull bank statements, GST filings, and ITRs, flag gaps, run background checks, and assemble the credit note in about a minute where a human took two hours. The credit manager still decides.
6. “Know Your Agent” is the next identity problem
If customers start deploying their own AI agents to interact with banks, then every assumption in the identity stack needs revisiting.
There is no human present for two-factor authentication. Entitlements have to be scoped to an agent acting on a person’s behalf. And a customer may soon operate dozens of agents, which raises a question no one had an answer for: how do you link each agent back to a single customer identity? The ‘Trust Without Friction’ panel called for a unique agent identifier analogous to a CIC and described it as an urgent, unsolved problem.
Regulators are already sketching the shape of the answer. MAS published its SAFER framework (Safeguards for Agentic Finance at Runtime) in July, covering agent identity and authority, pre-execution evaluation of actions, and audit records. EU and UK frameworks require the ability to reverse agent actions where possible. Indian regulators want “permissible agents”: know which agents are deployed, for what objective, and what they are doing. RBI’s FREE AI framework centres on accountability, fairness, resilience, and trust, and the “3 As” attributed to the SBI chairman (accuracy, accountability, anti-bias) were quoted in at least two panels.
One caution from the SEBI-side discussion: agentic systems spawn sub-agents dynamically, so guardrails on what data an agent can collect matter more than guardrails on how the model behaves. Data governance before agent governance. And the liability question (developer, organisation, or individual when an autonomous agent breaks the law) remains open.
7. Aadhaar’s next act: in-app face auth, selective disclosure, and DPDP
The ‘Digital Identity and Beyond’ session was described by panelists as the biggest revelation of the week for fintech. UIDAI is launching a face authentication SDK that allows Aadhaar authentication inside a business’s own app, with no redirect to a browser or the Aadhaar app, and localised to the requesting institution’s infrastructure so the central system is not exposed. For anyone who has watched drop-off spike at the redirect step, this removes the last major friction point in digital onboarding.
Equally significant is selective, purpose-driven data sharing: a user can share age only, or address only, rather than the full card. That maps directly onto the Digital Personal Data Protection Act, which comes into force in May 2027 and makes businesses liable for collecting only what they need. UIDAI also confirmed it is addressing geofencing through the SDK so Indians abroad can authenticate via a bank’s localised server, has a post-quantum cryptography roadmap underway (public/private key vulnerability expected within five years), and is building sovereign infrastructure targeting 25 to 30 times current capacity.
The Chairman of UIDAI, Mr. Neelkanth Mishra, acknowledged that OTP mismatch failures still reach end users without clear error codes, and said partner-facing communication is the gap. And the idea of agents holding purpose-scoped Aadhaar credentials (an address-only agent for hotel check-in, an age-only agent for age-gated services) was raised and received warmly, which connects this back to KYA.
Cross-regulator KYC acceptance across SEBI, RBI, and IRDAI has been agreed at FSDC level, with One Nation One KYC and the Account Aggregator framework as the portability layers.
8. AI is widening the credit funnel, in more languages and on more devices
The inclusion story at GFF was specific rather than aspirational. 22.9 crore people were inducted into credit last year, many new-to-credit. Bureaus cannot help with that cohort because they only see lender-submitted history, so the action has moved to unstructured data: transaction narrations, digitised physical documents, gig platform history, app-captured location, and Account Aggregator flows.
Panelists of ‘End-to-End AI in Credit’ put India seven to eight years ahead of Southeast Asia on model deployment maturity, and said those markets are leapfrogging by adopting India’s approaches directly. BCG’s flagship report estimated AI could unlock financial inclusion for 400 million additional Indians and deliver 100-plus basis points of ROA improvement to Indian financial institutions.
Voice was the interface that came up most. ONDC described a network participant testing a voice assistant that helps autorickshaw drivers in Bengaluru invest ₹20 in mutual funds. Open Financial Technologies pitched agentic voice for MSMEs to manage GST credit, vendor payments, and payroll in natural language, with approvals routed through a companion app. SBI’s design constraint for all of it: channel-agnostic, language-agnostic, and connectivity-aware, because 150 to 160 million Indians are still on feature phones and the system has to work over USSD and IVR.
The model choice is shifting too. Regulated institutions are gravitating to smaller, specialised, domain-specific models they can control: KFintech built its own system on open-weight Qwen models to keep sensitive data in-house, Mastercard’s AI Garage built a large tabular model for transaction data, and Revolut India built a transformer family to read financial histories as temporal signals. The right model for the job, rather than the biggest one.
What this means for You
Pulling it all together, four things are worth acting on now.
- Assume your video KYC and basic liveness can be beaten, and add detection that models generation techniques rather than specific models.
- Treat onboarding as the start of a risk profile, not the end of one, and find out where fraud, AML, and cyber signals live in your organisation before trying to connect them to anyone else’s.
- Decide, explicitly, where your agents stop, using something like SBI’s impact-stakes-reversibility test, and build evals before the next system prompt change.
- And get ahead of two dates: DPDP in May 2027, and RBI’s liability shift in January 2027.
The industry left Mumbai in agreement on the direction. The competition now is on speed, and the attacker already has a head start. Like our ghost kept causing mischief in Mumbai, other less entertaining fraudsters may be causing havoc in your systems. We can show you how to stay ahead of them on a single call!